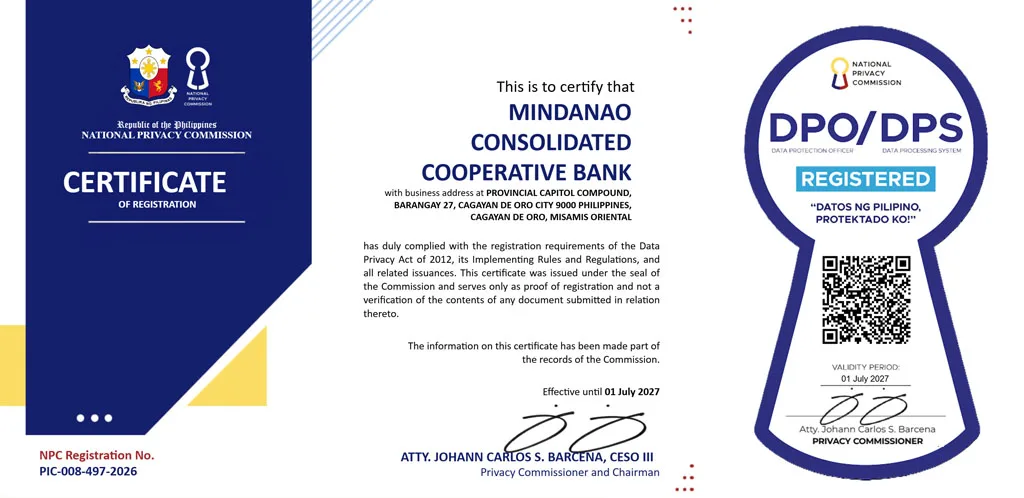

MINDANAO CONSOLIDATED COOPERATIVE BANK (MCCB) respects and values the CLIENT’s right to privacy with utmost importance. The Bank takes the necessary steps to protect and secure its CLIENTS’ personal information and their use of the Bank’s services.
As provided by the Data Privacy Act of 2012 (“DPA”), its Implementing Rules and Regulations (“IRR”), and issuances of the National Privacy Commission, the Bank guarantees compliance with all the requirements mandated by law, as well as with generally accepted global data protection standards and regulations. The Bank ensures the continued protection of the CLIENT’s personal information through organizational, physical, and technical measures for data protection, including policies for the evaluation, monitoring, and review of operations and security risks.
This Privacy Policy informs CLIENTS of updates to the Bank’s corporate policies on the collection, use, storage, disclosure, and disposal of personal information received and collected from customers, payees, users, and any individual who communicates with the Bank, raises inquiries and concerns, or transacts through authorized representatives, bank branches, official websites and platforms, and web-based applications and channels.
This Privacy Policy shall be subject to changes relative to policies and the law. The Bank shall notify CLIENTS of such changes by posting them on the Bank’s website and through other means of communication for the CLIENTS’ information and reference.
Clients’ privacy and the law
The Data Privacy Act of 2012 recognizes three broad classes of information:
- Personal information
- Any information, whether recorded in a material form or not, from which the identity of an individual is apparent or can be reasonably and directly ascertained by the entity holding the information, or which, when put together with other information, would directly and certainly identify an individual.
- Sensitive personal information
- Any attribute of a person’s personal information that can discriminate, qualify, or classify them, such as age, date of birth, marital status, government-issued identification numbers, account numbers, and financial information.
- Privileged information
- Any and all forms of information which, under the Rules of Court and other pertinent laws, constitute privileged communication — for example, lawyer–client, priest–confessor, or doctor–patient communications.
Your rights as a data subject
Under the Data Privacy Act of 2012, CLIENTS have the following rights:
- Right to be informed. The CLIENT may demand details as to how their personal information is being or has been processed by the Bank, including the existence of automated decision-making and profiling systems.
- Right to access. Upon written request, the CLIENT may demand reasonable access to their personal information, which may include the contents of the processed personal information, the manner of processing, the sources from which it was obtained, and the recipients and reason for disclosure.
- Right to dispute. The CLIENT may dispute inaccuracy or error in their personal information in the Bank’s systems through contact center representatives.
- Right to object. The CLIENT may suspend, withdraw, or remove their personal information from certain further processing upon demand, including the right to opt out of any commercial communication or advertising from the Bank.
- Right to data erasure. Based on reasonable grounds, the CLIENT has the right to suspend, withdraw, or order the blocking, removal, or destruction of their personal data from the Bank’s filing system, without prejudice to the Bank’s continuous processing for commercial, operational, legal, and regulatory purposes.
- Right to secure data portability. The CLIENT has the right to obtain from the Bank their personal information in an electronic or structured format that is commonly used and allows for further use.
- Right to be indemnified for damages. As a data subject, the CLIENT has every right to be indemnified for any damages sustained due to a violation of their right to privacy through inaccurate, false, unlawfully obtained, or unauthorized use of their information.
- Right to file a complaint. The CLIENT may file a complaint or raise any concern at any of our branches or at the Bank’s Head Office at MCCB Building, Capitol Compound, Luna–Velez Street, Cagayan de Oro City 9000, or get in touch with our Customer Relations Officer at customersupport@mccb.com.ph.
Collection and use of client personal information
MCCB collects and processes the personal information of CLIENTS only upon express consent — any freely given, specific, and informed indication of will by which CLIENTS agree to the collection and processing of their personal, sensitive, or privileged information. The Bank processes the CLIENTS’ personal information in accordance with the law, this Privacy Policy, the Terms and Conditions, and other legal instruments which the CLIENT may have entered into with the Bank.
As mandated by the Bangko Sentral ng Pilipinas, in the usual course of banking business, the Bank collects the following personal information from and about the CLIENT, including, but not limited to: full legal name, gender, date of birth, nationality, civil status, permanent address, present address, tax identification number (TIN) and other government-issued identification numbers, mobile number, home number, personal email address, office contact details, company name, job position or rank, office address, source of funds, and gross annual income, among others.
When a CLIENT provides the Bank with personal information by which they can be reasonably identified, they can be assured that it will be used only in accordance with this Privacy Policy and the relevant Terms and Conditions governing their relationship with the Bank. The Bank collects the CLIENT’s personal information from the following sources:
- their Personal Information Sheet;
- information collected by the Bank about the CLIENT upon contacting through authorized representatives in bank branches and contact centers, email, mobile applications or services, and other online and mobile platforms; and
- information collected about the CLIENT from public records and from other available sources authorized to disclose their information.
All personal information collected by the Bank about the CLIENT may be combined and processed to improve its products, services, and communications. The Bank ensures that only authorized employees and third-party service providers — who have undertaken to satisfy the Bank’s stringent corporate, legal, information security, and data privacy requirements — are allowed to process the CLIENT’s personal information. Through the CLIENT’s express consent, the Bank may disclose personal information to third-party service providers who perform business operations on the Bank’s behalf, to partners who collaborated to provide services to CLIENTS, and to business partners that provide joint communications which may be of interest to the CLIENT.
By registering, signing in to, or using the Bank’s consent forms for products, services, and applications, CLIENTS authorize and consent to the processing, sharing, and/or transferring by the Bank of personal information relating to their accounts for specified purposes which, in all cases, comply with or are pursuant to the Bank’s legal or contractual obligations:
- Government regulatory agencies, credit information or investigation companies, financial institutions, credit bureaus, other banks, credit card companies, loyalty program partners, and consumer reporting or reference agencies such as the Cooperative Bank Federation of the Philippines (BANGKOOP), the Credit Information Corporation (CIC), and the TransUnion Credit Bureau, for the purpose of credit investigation, consumer reporting, or for reports of the CLIENT’s credit history and account updates;
- Third persons, correspondent banks, service providers, and entities as the Bank deems necessary to enable it to service the CLIENT’s account/s and to provide all the existing features of the account/s, the Bank’s products, services, facilities, and channels, and any future enhancements thereto, or to assist the Bank in the processing of data, including its collection, recording, organization, storage, management, protection, updating or modification, retrieval, consultation, use, consolidation, blocking, erasure, or destruction;
- Third parties engaged by the Bank or by its subsidiaries or affiliates for the purpose of direct or indirect marketing to offer selected products and services which may interest the CLIENT, unless specifically instructed otherwise in writing;
- Insurers, insurance brokers, or providers of deposit or credit protection or protection against all kinds of risks;
- Republic Act No. 9510, or the Credit Information Systems Act, and its Implementing Rules and Regulations, which mandate the Bank to submit the CLIENT’s credit data to the Credit Information Corporation (CIC) and share the same with other accessing entities and special accessing entities authorized by the CIC;
- Bangko Sentral ng Pilipinas Circular No. 472, Series of 2005, as implemented by Bureau of Internal Revenue Regulation No. 4-2005, which mandates the Bank to conduct random verification with the Bureau of Internal Revenue in order to establish the authenticity of the Income Tax Return (ITR), accompanying financial statements, and such other documents, information, and data;
- The National Internal Revenue Code, as amended, which mandates the Commissioner of Internal Revenue to inquire into the bank accounts of the following taxpayers: a) a decedent, in order to determine their gross estate; b) a taxpayer who has filed an application to compromise their tax liability on the ground of financial incapacity; and c) a taxpayer whose account information is requested by a foreign tax authority;
- Unexplained wealth under Section 8 of Republic Act No. 3019, or the Anti-Graft and Corrupt Practices Act;
- Cases under Republic Act No. 9160, or the Anti-Money Laundering Act of 2001, when there is probable cause that the deposits or investments involved are in any way related to an unlawful activity or a money laundering offense;
- Regulatory authorities and such other persons or entities the Bank may deem to have the authority or right to such disclosure of information, as in the case of regulatory agencies, government or otherwise, which have required such disclosure from the Bank and when the circumstances so warrant; and
- Other related and applicable laws and regulations, subject to the CLIENT’s right to information under the Data Privacy Act, which legally mandate the Bank to obtain and disclose their personal information to government regulatory agencies and consumer reporting or reference agencies.
The CLIENT’s personal information provided to the Bank shall only be used for the purpose of the service and product delivery consented to, subject to the Terms and Conditions agreed to. With express consent, the CLIENT may agree and authorize the Bank to share personal information with private entities subject to mandatory disclosure pursuant to government and public functions. In all instances, the Bank processes and/or discloses personal information in accordance with the Data Privacy Act and its Implementing Rules and Regulations.
Data storage
It is the policy of the Bank that all systems, storage media, and repositories that store customer data shall have completed the appropriate information security, risk, legal compliance, and privacy impact assessments. The CLIENT’s personal information shall only be stored in the Bank-managed environment. Physical copies of documents containing the CLIENT’s personal information shall be stored in physical vaults in a sealed and secure manner. All systems, storage media, and repositories which are used, and will be used in the future, to store personal information are and will be duly approved and registered with the Bangko Sentral ng Pilipinas and other regulatory agencies, as the case may be.
Data access and retrieval
Access refers to a user’s capacity to access or retrieve data stored within a database or other repository. The CLIENT’s personal information can only be accessed and retrieved by authorized personnel of the Bank, and only pursuant to a legitimate business purpose, in accordance with the consent provided to the Bank. Remote connectivity to any Bank-managed environment is only through Virtual Private Network or Access Gateway technology solutions that enable the Bank to enforce the security controls required to protect the CLIENT’s personal information.
Data retention
Regulation, legitimate bank business purpose, and policy define the data retention period for the CLIENT’s personal information. Pursuant to Section X808 of the Manual of Regulations for Banks issued by the Bangko Sentral ng Pilipinas, transaction records shall be maintained and safely stored for five (5) years from the date of the transaction, except where specific laws and/or regulations require a different retention period, in which case the longer retention period is observed. Pursuant to Bureau of Internal Revenue Regulation 17-2013, documents pertaining to the CLIENT’s billing statements, which indicate taxable transactions, shall be preserved for ten (10) years.
Further, the Bank keeps the CLIENT’s personal information for as long as it is necessary:
- for the fulfillment of the declared, specified, and legitimate purposes provided above, or when the processing relevant to those purposes has been terminated;
- for the establishment, exercise, or defense of legal claims; or
- for legitimate business purposes, in accordance with the standards of the banking industry.
Data disposal
The Bank has established mechanisms for the secure disposal of data from its systems once the data is no longer required by the business for any legitimate purpose and activity. After the defined retention periods, the Bank shall dispose of the CLIENT’s personal information in a secure manner in order to prevent further processing, unauthorized access, or disclosure to any other party.
Personal data breach management
A personal data breach refers to a breach of security leading to the accidental or unlawful destruction, loss, alteration, or unauthorized disclosure of, or access to, personal data transmitted, stored, or otherwise processed. A personal data breach shall be subject to notification requirements under the following conditions:
- the compromised data involves personal data that may be used to enable identity fraud;
- there is reason to believe that the information may have been acquired by an unauthorized person; and
- the unauthorized acquisition is likely to give rise to a real risk of serious harm to any affected data subject.
The Bank shall notify the National Privacy Commission and affected customers in case of a breach within 72 hours upon knowledge of, or reasonable belief by, the Bank or its third-party processor that a personal data breach has occurred. If such an event occurs, the Bank shall notify the CLIENT, through a secure means of communication, of the nature of the breach, the personal information possibly compromised, the measures taken to address the breach and reduce negative consequences, and the contact details of the government authorities concerned who can assist in mitigating the possible ramifications that can compromise the CLIENT’s right to privacy.
Questions about your personal data?
For inquiries, complaints, and other concerns, write to the Bank’s Compliance Officer at compliance@mccb.com.ph or reach our Customer Relations Officer at customersupport@mccb.com.ph.
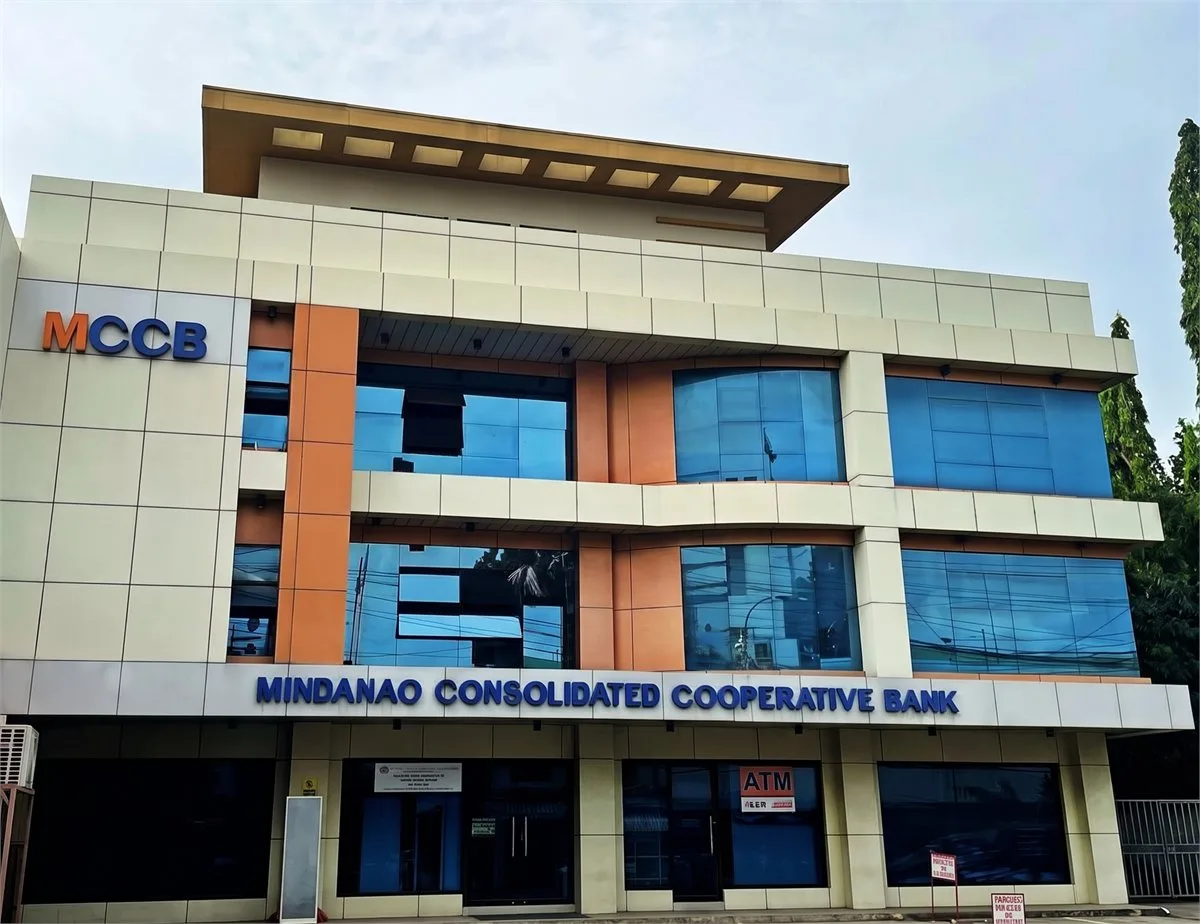
MCCB Building, Gen. A. Luna St. corner Don A. Velez St., Provincial Capitol Compound, Barangay 27, Cagayan de Oro City 9000
 Bangko Sentral
 Deposit insured
 Cooperative Dev.
 BancNet
 InstaPay